CASE STUDY
OWASP ZAP Security Assessment
A web application security assessment using OWASP ZAP to identify potential security issues and evaluate the security posture of a controlled test environment.
Project Overview
The OWASP ZAP Security Assessment project involved performing a web application security assessment in a controlled cybersecurity lab environment.
The assessment was designed to demonstrate practical vulnerability assessment techniques and the use of OWASP ZAP for identifying potential security issues.
The Challenge
Web applications can contain security weaknesses that may expose sensitive information or increase the risk of unauthorized access.
The objective was to assess a web application in a controlled environment and identify potential security concerns without affecting a production system.
The Solution
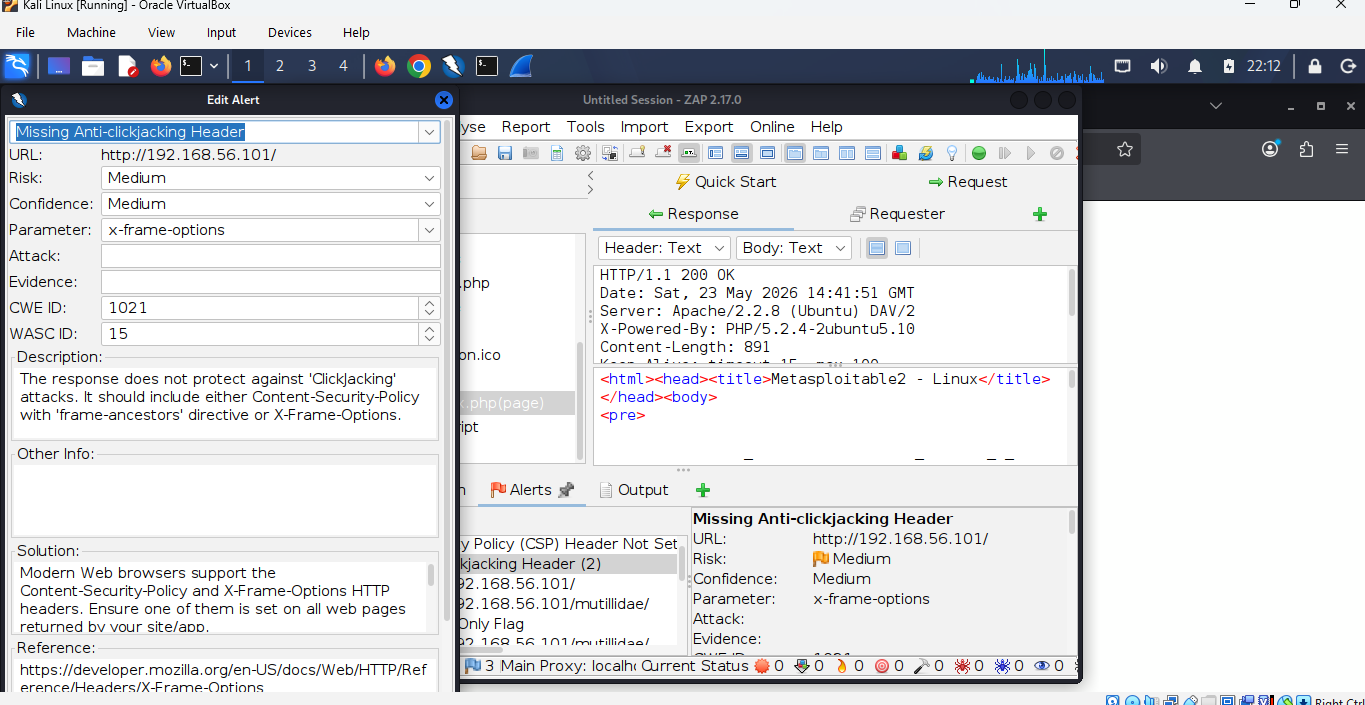
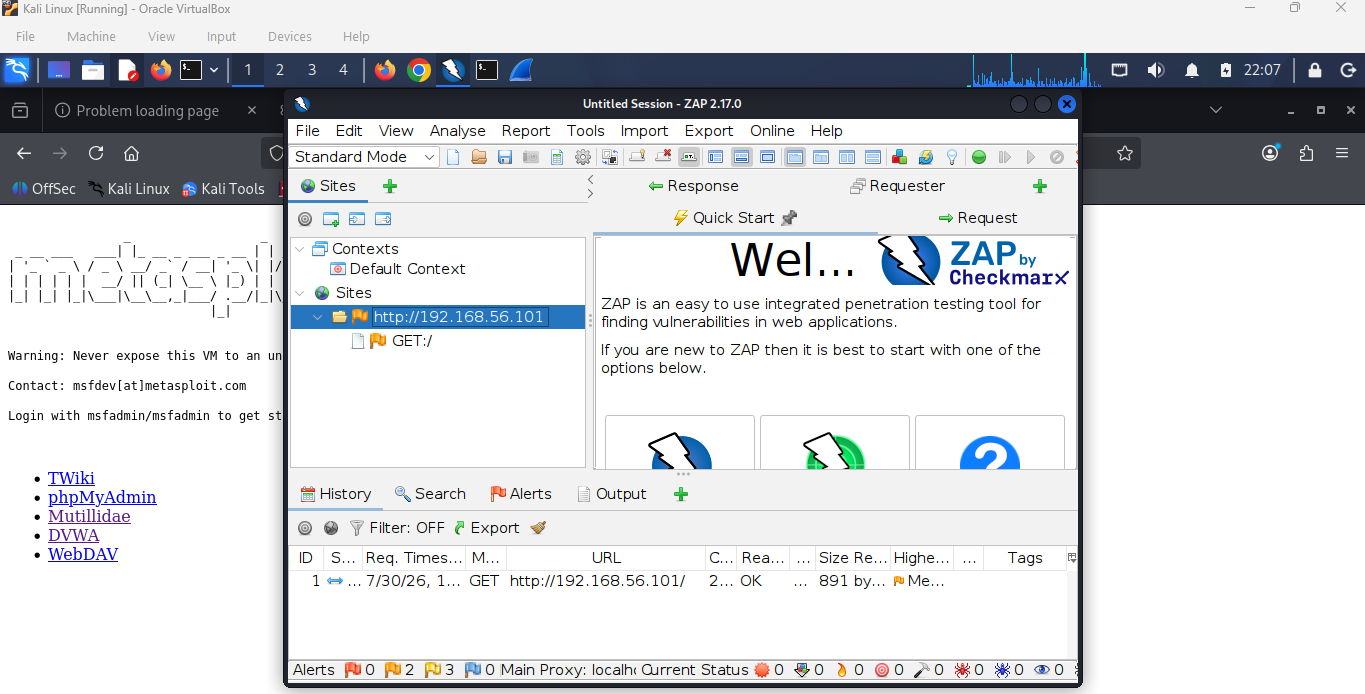
OWASP ZAP was configured and used to perform a passive web security assessment against the test application.
The assessment involved observing application traffic, reviewing security alerts, analyzing discovered resources, and documenting findings.
The project was performed using a controlled virtual lab environment containing Kali Linux and a deliberately vulnerable test application.
Key Features
- OWASP ZAP security assessment
- Passive web application scanning
- Security alert analysis
- Vulnerability identification
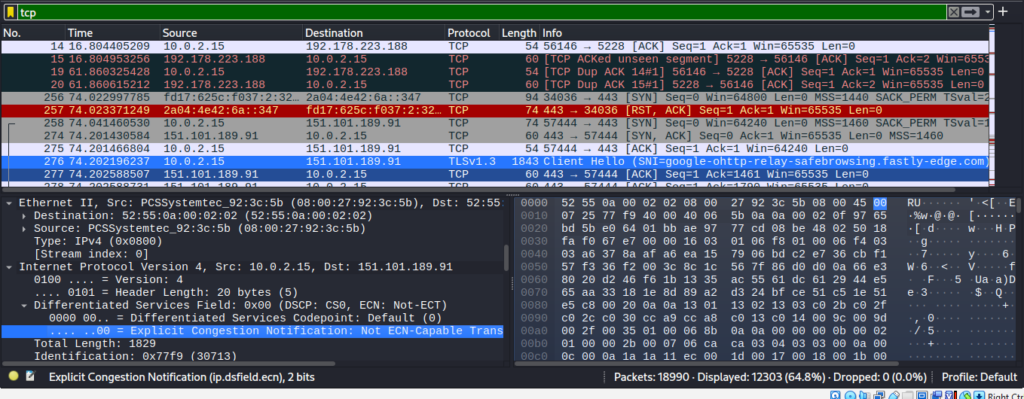
- HTTP traffic inspection
- Controlled penetration-testing laboratory
- Kali Linux
- Metasploitable
- Security findings documentation
- Security remediation recommendations
Outcome
The assessment demonstrated a practical workflow for identifying and documenting web application security issues using OWASP ZAP.
The findings were used to develop security recommendations focused on reducing vulnerabilities and improving the overall security posture of the test application.
TECHNOLOGIES
Built with the right tools.
OWASP ZAP
Kali Linux
Metasploitable
VirtualBox
HTTP
Web Security
PROJECT GALLERY
A closer look at the project.